Odudu: an identity provider that proves its own conformance
A multi-tenant OAuth and OpenID Connect provider, with an admin console, brandable sign-in pages and an MCP server so agents can operate it under the same capabilities as everyone else.
- Problem
- Every product needs sign-in; teams that run their own want to keep their users' data on their own servers.
- Approach
- Standards first, many tenants kept apart by the database, decisions recorded as ADRs.
- Result
- The OpenID Foundation conformance suite runs in CI on every change.
How it fits together
Apps and agents connect to Odudu. It serves the standard OpenID Connect and OAuth 2.0 endpoints, an admin API with more than a hundred operations, an admin console, and an MCP server.
Agents reach the admin API through the MCP server and are held to the same capabilities as everyone else.
Many tenants, one container
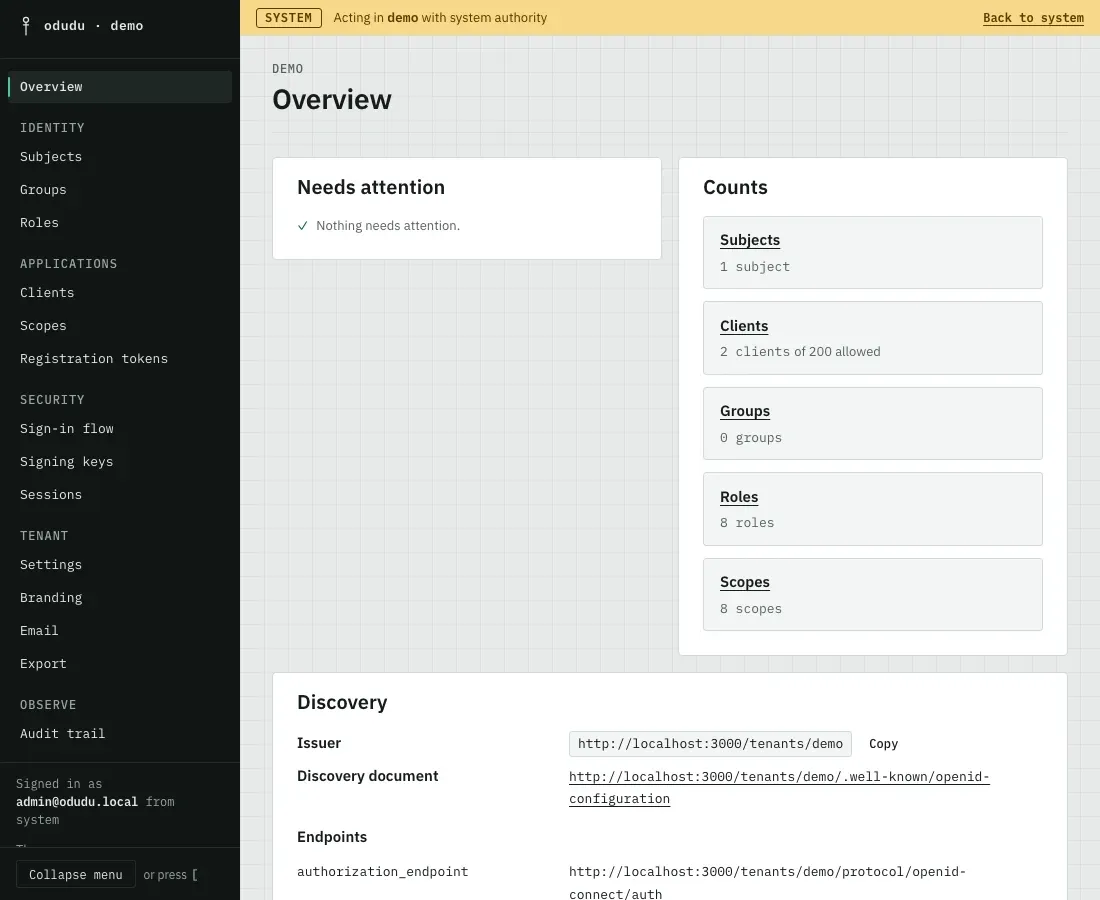
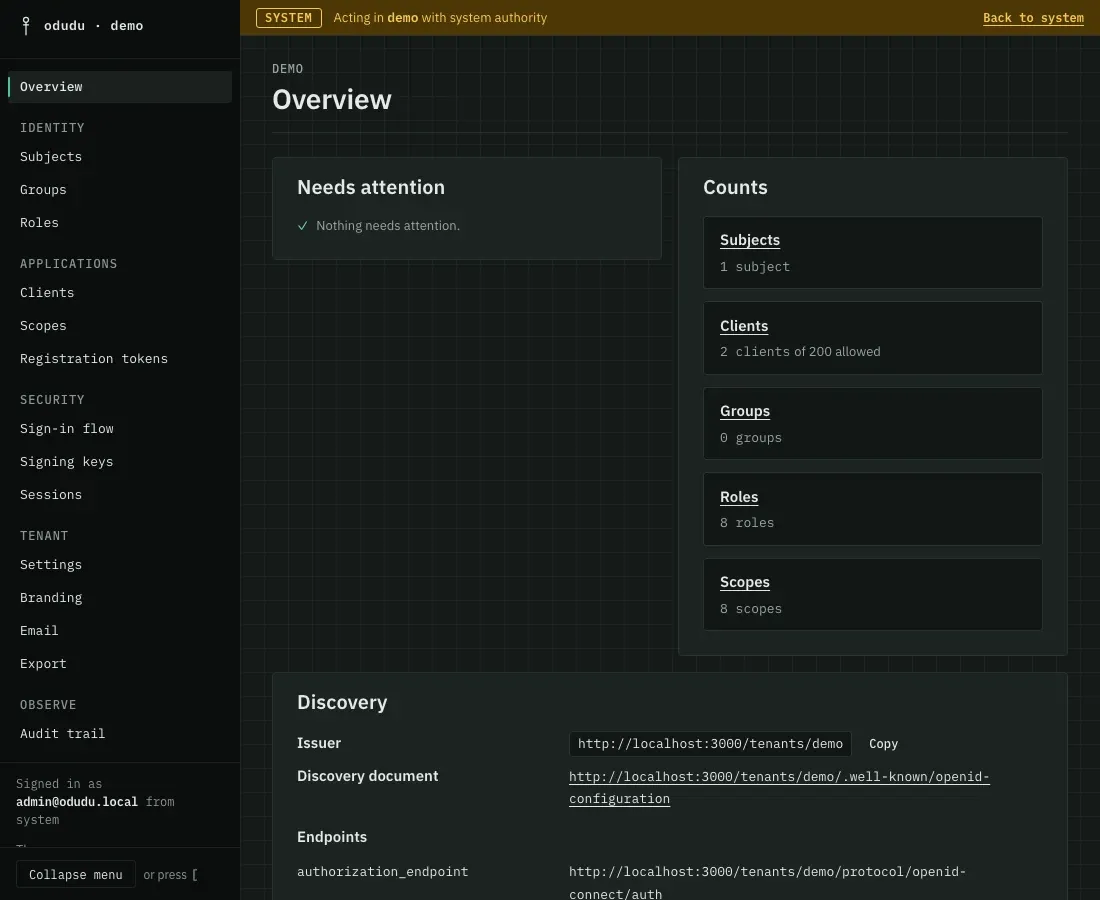
Many tenants run in one container with PostgreSQL, kept apart by the database itself. Every page the server shows, and its mail, can use a tenant's theme and a client's branding, in light and dark.
The admin console
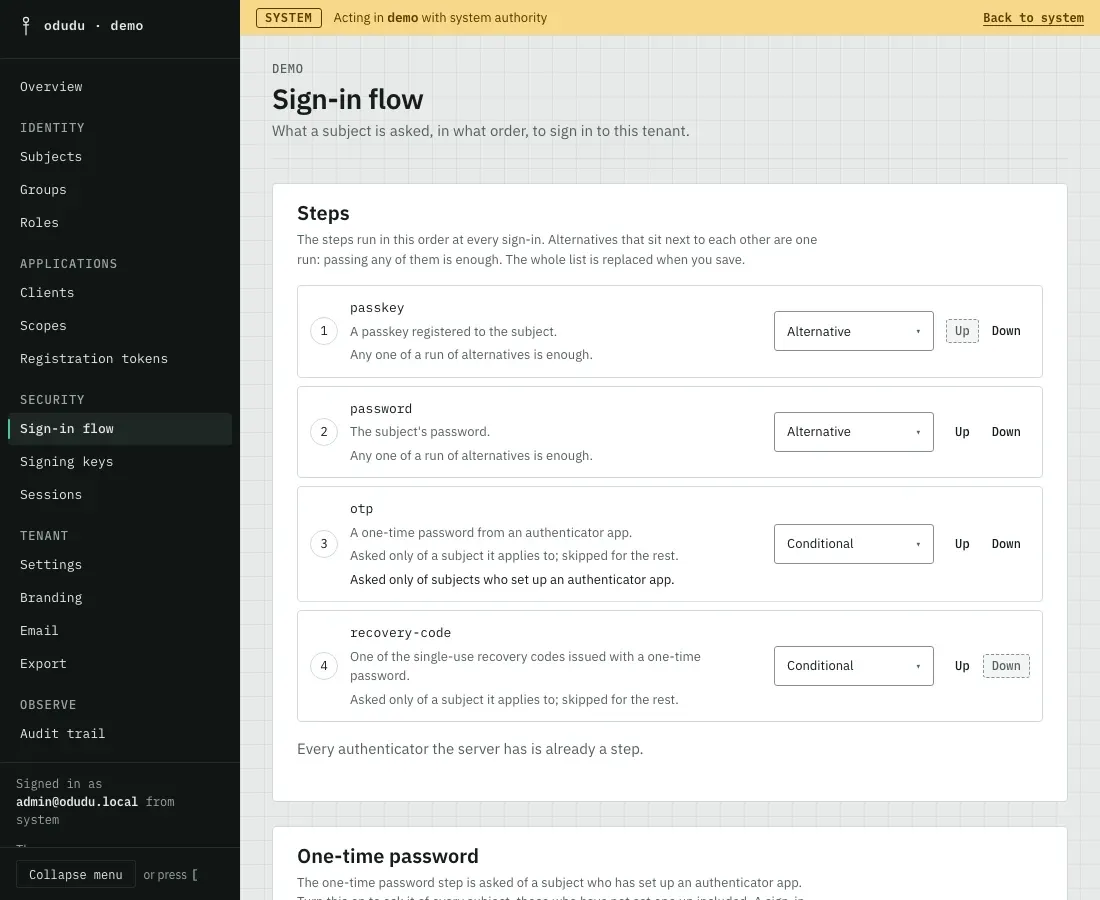
The console has a page for every area of the admin API. It is tested in CI with Playwright and axe against WCAG 2.2 AA, in light and dark themes.
Conformance as a test, not a badge
The OpenID Foundation conformance suite (Config OP) runs in CI. A change that breaks the protocol fails the build, the same as a broken unit test.
Status
Odudu is before 1.0, a release candidate, and has not had an independent security review yet.